
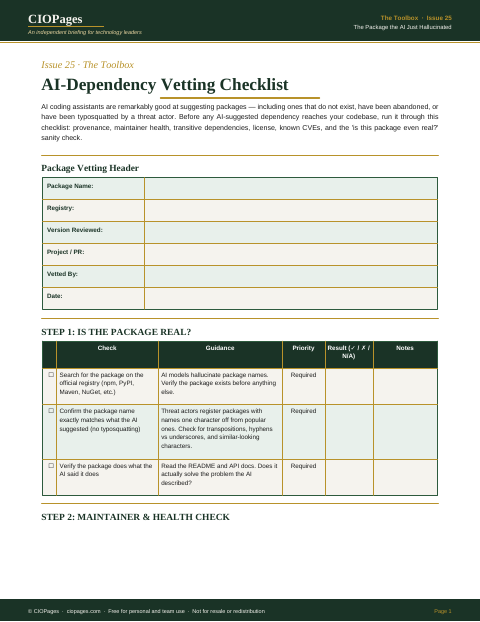
What's inside
- A header for the package, registry, version, pull request, reviewer and date.
- Step 1, is the package real: registry search, typosquatting check and whether it does what the AI said.
- Steps 2 and 3, maintainer health and license: last commit, maintainer count, ownership transfers, license compatibility and license changes.
- Steps 4 and 5, vulnerabilities and supply chain: CVE scans including transitive dependencies, SBOM update, build provenance, install scripts and version pinning.
- Step 6, internal approval against your approved dependency list.
- A sample vetting log of five packages, including one an AI made up.
Format: PDF (4 pages).
How to use it
Run each AI-suggested dependency through it before the pull request that adds it is merged, and note the result in the pull request.
Get the checklist
It is free. We email the download link to your work address.