
What's inside
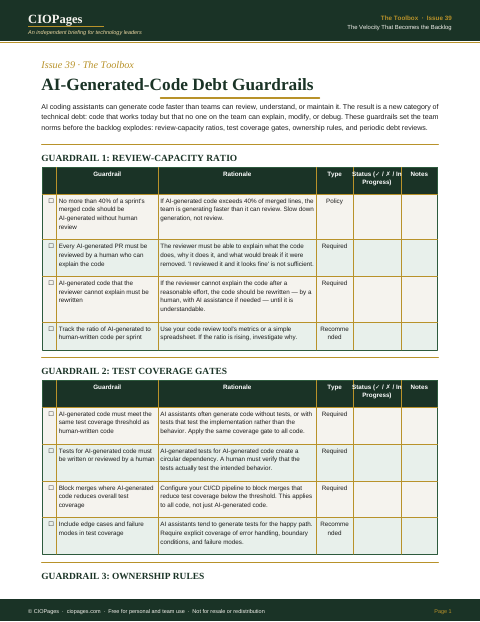
- Guardrail 1, review capacity: a ceiling on the share of AI-generated code per sprint and reviewers who can explain the code.
- Guardrail 2, test coverage: the same coverage gate for all code, human review of AI-written tests, and merge blocking.
- Guardrail 3, ownership: a named owner for each AI-generated file, recorded in CODEOWNERS or equivalent, with documented transfers.
- Guardrail 4, periodic debt review: a quarterly review, a four-level risk classification and a share of each sprint for remediation.
- Guardrail 5, dependency vetting: vetting, version pinning and vulnerability scanning in CI/CD.
- Each guardrail is marked Policy, Required or Recommended, with a status column.
- A policy summary table: each guardrail, its policy and how it is enforced.
Format: PDF (3 pages).
How to use it
Agree the thresholds with the team, adapt the policy summary, and check the guardrails at each quarterly debt review.
Get the policy and checklist
It is free. We email the download link to your work address.